- Trezor warned users not to click on links in fraudulent emails.
- BitBox said its email provider was likely hacked.
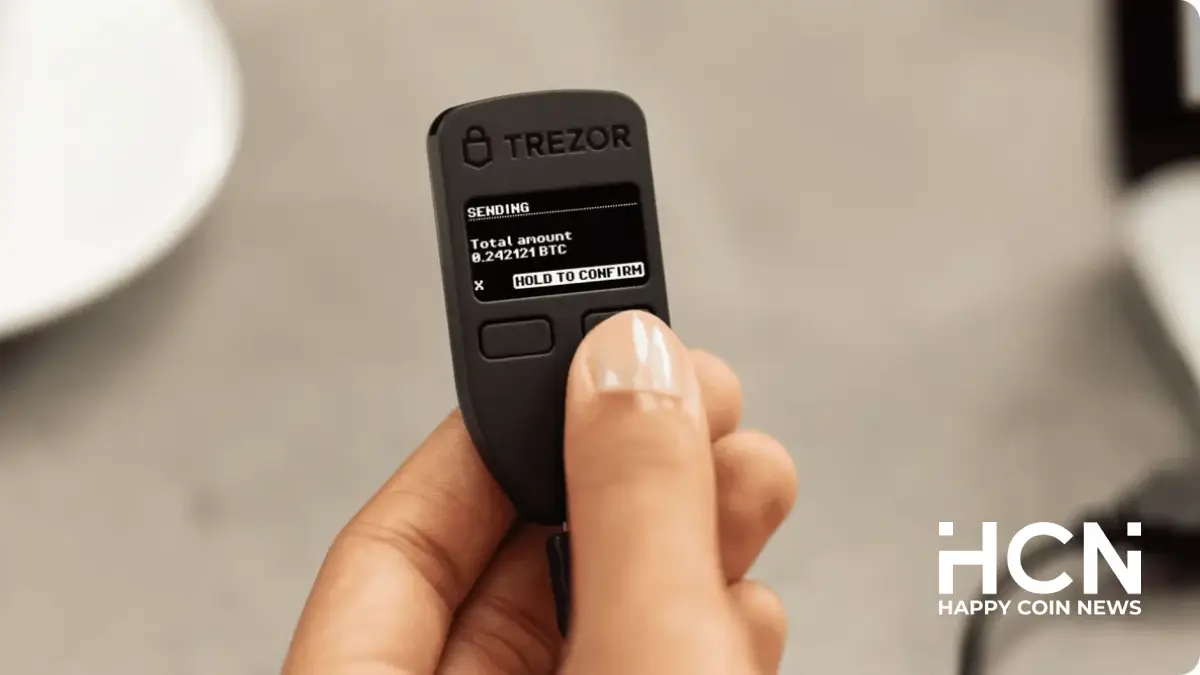
A representative of hardware wallet maker Trezor announced that its third-party supplier had been hacked. Users were warned that an email with the subject line "Critical Security Alert: STM32 Entropy Vulnerability" was a phishing attempt. The company urged users not to click on the links and stated that it was investigating the situation.
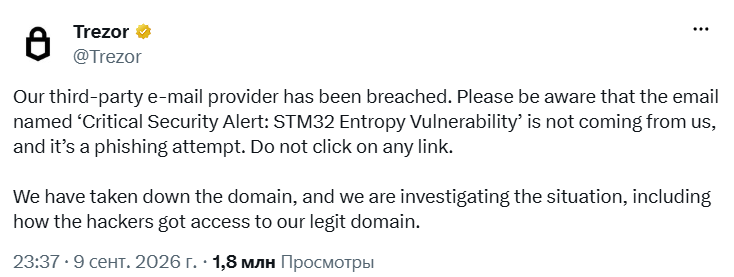
Source: X
The phishing message in question was intended to convince users that a serious vulnerability had been discovered in the STM32 microcontrollers used in the devices. This vulnerability could result in the generation of recovery phrases without sufficient randomness, potentially putting users' funds at risk.
Along with Trezor, BitBox device owners received warnings about a phishing attack. The company stated that its newsletter provider had likely been compromised.
This isn't the first time a third-party partner of Trezor has suffered a security breach. In August, the platform reported a similar incident involving its logistics partner ShipMonk, which resulted in the personal data of nearly 14,000 customers being exposed. On September 4, Trezor reported that an additional 67,000 customers in the US were affected.
The information on this site is for informational and educational purposes only and does not constitute investment advice or financial recommendations. Cryptocurrencies and digital assets carry a high level of risk, including possible loss of capital. The editors are not responsible for decisions made based on the published materials. It is recommended to conduct your own research (DYOR) before making investment decisions. Read the editorial policy at https://happycoin.news/about/